EN/IT
Risk Management and Mitigation Solutions

Risk Management and Mitigation Solutions

WWG’s IT risk management services identify what can stop or damage the software your revenue depends on, estimate the impact and likelihood of each event, and act in order of severity. Senior engineers examine technical failure, security exposure, vendor dependencies and loss of internal knowledge, and hand you a risk register with an owner and a countermeasure for each entry. It is for CEOs, CTOs and IT managers who have to answer the board, customers or an auditor.

Definition

What are IT risk management services

IT risk management services are the work of identifying what can stop or damage a company’s software systems, estimating the impact and likelihood of each event, and acting in order of severity. Applied to production software, they cover technical failure, security exposure, dependence on vendors and external components, and loss of internal knowledge, and they produce a risk register with an owner and a countermeasure for each entry.

specializations

What we offer

Risk Assessment

Perform in-depth evaluations to uncover potential vulnerabilities across your business.

Mitigation Strategies

Develop customized plans to reduce identified risks and safeguard your assets.

Continuous Monitoring

Utilize real-time tracking systems to detect and address emerging threats proactively.

Crisis Management

Implement effective strategies and tools for managing and recovering from unforeseen disruptions.

Regulatory Compliance

Ensure alignment with legal requirements and industry standards, such as GDPR, HIPAA, and PCI-DSS.

our advantages

Why Choose WWG for Risk Management?

01

Expertise Across Industries

Extensive experience managing complex risk scenarios in finance, healthcare, technology, and manufacturing.

02

Proactive Risk Prevention

Identify and mitigate risks before they impact your business operations.

03

Customized Solutions

Strategies tailored to align with your business goals and sector-specific challenges.

04

Innovative Risk Tools

Leverage advanced technologies and analytics for accurate risk evaluation and monitoring.

Empowering Your Business with Seamless Infrastructure ManagementEmpowering Your Business with Seamless Infrastructure ManagementEmpowering Your Business with Seamless Infrastructure ManagementEmpowering Your Business with Seamless Infrastructure ManagementEmpowering Your Business with Seamless Infrastructure ManagementEmpowering Your Business with Seamless Infrastructure ManagementEmpowering Your Business with Seamless Infrastructure ManagementEmpowering Your Business with Seamless Infrastructure Management

process

How Do We Work?

01

Risk Identification

Identify potential risks through comprehensive evaluations of your business environment.
02

Risk Analysis

Using data-driven methodologies, assess the likelihood and impact of identified risks.
03

Mitigation Planning

Create and implement strategies to minimize vulnerabilities effectively.
04

Implementation

Deploy tools and solutions to safeguard your operations from potential disruptions.
05

Ongoing Support

Provide continuous monitoring and periodic reviews to adapt strategies to evolving risks.

technologies

Technologies we use

JavaScriptJavaScript
TypeScriptTypeScript
ReactReact
AngularAngular
Next.jsNext.js
NodeJSNodeJS
ExpressJSExpressJS
NestJSNestJS
JavaJava
FlutterFlutter
AWSAWS
TerraformTerraform
AnsibleAnsible
DockerDocker
KubernetesKubernetes
PrometheusPrometheus
GrafanaGrafana
reviews

What Our Clients Are Saying

Clutch rating
"WWG's competencies in technical and management aspects were impressive."

WWG successfully delivered a project document and software that fully met RAG requirements. WWG's project management was efficient — they delivered everything on time. Moreover, they showcased clear communication and strong technical capabilities, which were key to the project's success.

Francesco Adinolfi

R&D, Innovaway SpA

Custom Software Development

WWG provided custom software development services for an ICT company. The team designed and developed an innovative ICT software system capable of supporting RAG services.

Paese
Naples, Italy

The engagement

IT risk management in concrete terms

Duration
Identification and analysis phase set in scoping, according to the perimeter. Ongoing support on a monthly basis.
Start
After the perimeter is agreed and access and incident history are in place.
Who does the work
Senior WWG engineers, with a named owner accountable for the engagement who remains the point of contact under ongoing support.
What you provide
Read access to code and infrastructure, incident history, list of vendors and licences, a few hours of interviews, one contact person.
Output
A risk register with impact, likelihood, owner and countermeasure for each entry, a mitigation plan ranked by severity, a hand-over session.
Format
Fixed-scope analysis. Implementation of countermeasures and ongoing support with monitoring and periodic reviews available separately.

The price of the analysis is set before we start, in the scoping conversation, based on the perimeter. Implementation is quoted on the mitigation plan; ongoing support runs on an agreed monthly fee. We do not publish a price list.

Comparison

IT risk management and the alternatives

When the question of what can stop the business comes up, four answers with similar names and different purposes are usually on the table. This table says what each one is for, so the choice is made on the question you need answered.

CriterioWWG IT risk managementRisk management platformInternal governance frameworkSecurity and compliance audit
Who it is forCEOs, CTOs and IT managers with a production system to protect.Risk and compliance functions managing registers and workflows at group level.Organisations that need to formalise roles, policies and accountability.Anyone who needs to know how exposed the system is today against regulation such as NIS2.
What it coversTechnical, security, supply and knowledge risk in production software.Recording and tracking of risks entered into it; not their technical identification.Processes and accountability; not the real state of code and infrastructure.Vulnerabilities, configuration and regulatory gaps at a given moment.
DurationAnalysis set in scoping; ongoing support on a monthly basis.In continuous use, with initial setup.Months to adopt, then permanent.Set in scoping, according to the perimeter.
What you getA risk register with owner and countermeasure, a mitigation plan, periodic reviews.A register to fill in and dashboards; the content is yours to produce.Policy documents and an organisational model.A ranked account of real exposure with the remediation required.
When it makes senseWhen you need to know what can break in the software that carries the business and what to do first.When the risks are already identified and you need to track them at scale.When a customer, a regulation or the board requires a formal structure.When the question is specifically about security and compliance.

The four options complement each other: WWG’s IT risk management produces the content that a framework or a platform then organises, and uses the security and compliance audit as one of its sources.

Published case studies

FAQ

Frequently Asked Questions

IT risk management is the work of identifying what can stop or damage a company’s software systems, estimating the impact and likelihood of each event, and acting in order of severity. Applied to production software it covers technical failure, security exposure, dependence on vendors and external components, and loss of internal knowledge. The result is a risk register with an owner and a countermeasure for each entry, not a policy document.
Risk management services are engagements in which people identify, analyse and mitigate risk for you; risk management software is a platform where risks that have already been identified are recorded and tracked. Searching for IT risk management services mostly returns the second, plus governance frameworks written for the organisation as a whole. This page is about the first, applied to production software: senior engineers who read code, infrastructure, vendors and team and tell you what can break, how likely it is, and what to do first. If you need a GRC platform or an enterprise framework, this is not the right page.
Risk management is critical because the software your revenue depends on does not stop with notice. A technical failure, an exploited vulnerability, a vendor that closes down or the only person who knows a system leaving all produce financial loss, operational disruption and reputational damage. Knowing in advance which of these events are likely and which are severe lets you act first, with proportionate countermeasures, instead of reacting to crises that could have been avoided.
The engagement covers four types of IT risk in production software. Technical risk: fragile architecture, technical debt, missing tests, infrastructure without redundancy. Security risk: vulnerabilities, misconfigurations, access and data handling. Supply risk: dependence on a single vendor, component or licence with no alternative. Knowledge risk: systems only one person can operate, and missing documentation. For each risk we estimate impact and likelihood and assign an owner and a countermeasure.
WWG reduces risk for your company in five steps. Identification: we evaluate the system, the infrastructure, the vendors and the team. Analysis: we estimate likelihood and impact for each risk from the data available, such as incident history and metrics. Mitigation planning: we define the countermeasures and their order. Implementation: we execute or support the changes. Ongoing support: we monitor and review the register periodically, because risks change with the system and with the market.
The duration of the identification and analysis phase is set in scoping, according to the perimeter: the number of systems, vendors and environments, and the incident history and documentation available. This phase is a fixed-scope engagement, with duration and price set before we start. Implementation of the countermeasures is quoted separately on the basis of the mitigation plan. Ongoing support, if you choose it, runs on an agreed monthly fee. We do not publish a price list.
Senior WWG engineers run the IT risk management engagement, with a named owner who is accountable for it through to delivery and, under ongoing support, over time. From you we need read access to code, infrastructure and configuration, the incident history, the list of vendors and licences, a few hours of interviews with the people who operate the system and the people accountable for it to the business, and one contact person. Your team keeps working as usual.
We have experience managing complex risk scenarios in finance, technology, healthcare and manufacturing, industries where production software carries processes that cannot stop and data that cannot be exposed. The method, that is identify, analyse, plan, implement and monitor, is the same in every industry; what changes are the priorities, the regulations that apply and the appropriate countermeasures, which we adapt to your context during the analysis phase.
Risk management strategies should be reviewed at least once a year and whenever a significant change occurs: a major release of the system, a change of vendor or infrastructure, the departure of a key person, a new applicable regulation, or an incident in production. Under ongoing support, periodic reviews are part of the engagement, so the risk register reflects the system as it is today rather than as it was at the time of the first analysis.
Yes. For clients under ongoing support, the named owner and the engineers who know the system are the point of contact when a risk materialises, and they work with your team to contain the incident, restore service and update the register with what was learned. For clients not under ongoing support, the mitigation plan delivered includes the countermeasure and the owner for each risk, so the response does not depend on improvisation in the moment.
After the risk analysis you receive the register with impact, likelihood, owner and countermeasure for each risk, the mitigation plan ranked by severity, and a hand-over session in which we defend every assessment. Then you decide: execute the countermeasures with your own team, hand them to others, or ask WWG for implementation and ongoing support with monitoring and periodic reviews. The analysis is a standalone engagement and does not commit you to continuing with us.
WWG’s IT risk management services are for companies with a production system their revenue depends on: CEOs and CTOs who have to answer the board or an auditor on what can stop the business, IT managers who inherited systems from a previous vendor without a view of the risks, companies that depend on a single person or a single vendor for a critical component. If the question is what can break and what to do first, this is the right engagement.

Related services

Where the risks come from

Technical risk surfaces by reading the source in a code audit, and regulatory exposure through a compliance and security review. Risk carried by the technologies themselves comes out of stack analysis.

Tell Us What's Broken
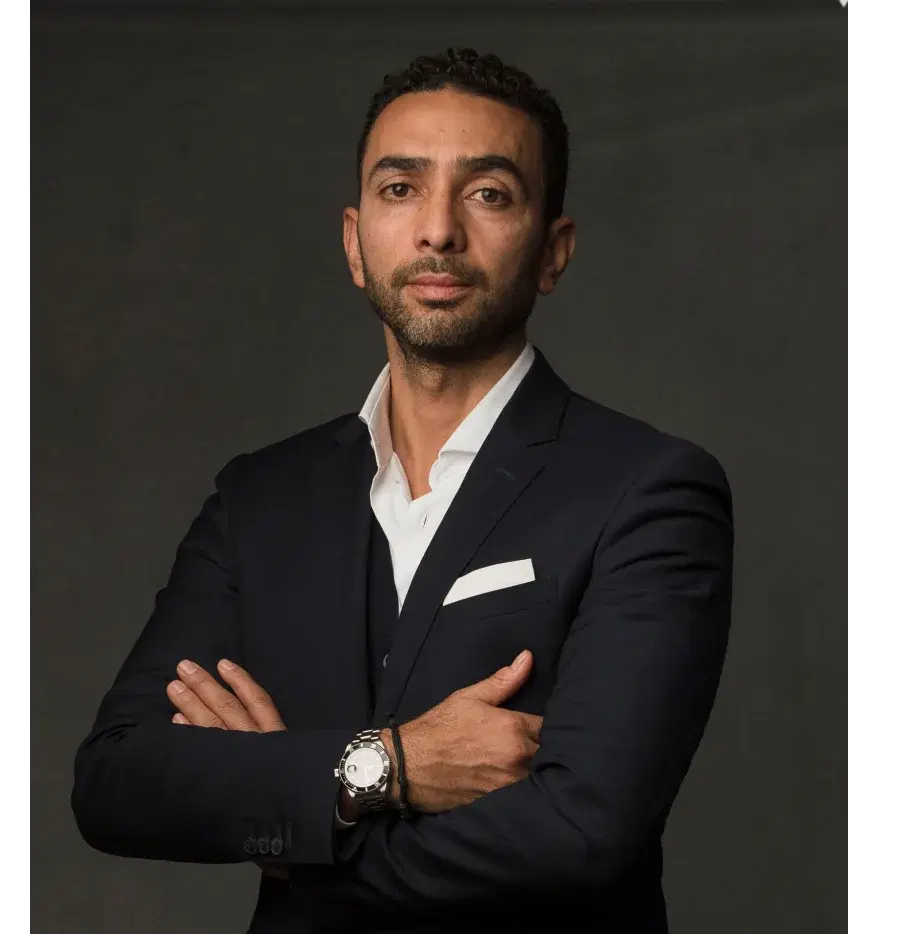
Mohamed Deramchi

Mohamed Deramchi

Founder & CEO of WWG

20+ years in IT leadership, product, and cloud consulting. Leads delivery strategy and senior technical direction.

AddressCorso Europa 15, 20122 Milano (IT)

Send Your Brief

By submitting you agree to our privacy policy.

Coesione Italia 21-27 Lombardia - Cofinanziato dall'Unione europea - Regione Lombardia