The Software Development Life Cycle, or SDLC, is the structured process used to plan, build, test, deploy and maintain software. For CTOs and engineering leaders, SDLC phases are not bureaucracy; they are the operating system for predictable delivery, secure-by-design engineering and accountable product investment.
TL;DR / Key Takeaways
- The seven core SDLC phases are planning, analysis, design, implementation, testing, deployment and maintenance.
- Agile, Waterfall, Spiral and V-Model are not rivals by default; each suits a different risk, governance and uncertainty profile.
- Security, compliance and maintainability must be designed into every SDLC phase, not bolted on before release.
- Hybrid SDLC models are often the pragmatic choice for European scale-ups and mid-market enterprises.
- The right SDLC model is the one your teams can execute consistently, measure objectively and improve continuously.
What is the Software Development Life Cycle and why do SDLC phases matter?
The Software Development Life Cycle is a repeatable framework for turning a business need into working, supported software. SDLC phases matter because they create shared checkpoints for scope, architecture, engineering, testing, release and improvement. Without them, teams rely on heroics, undocumented decisions and late-stage risk discovery.
According to ISO/IEC/IEEE 12207:2026, published in April 2026, the standard establishes a common framework for software life cycle processes and applies from conception through development, operation, support and retirement. It also states that lifecycle processes can be applied concurrently, iteratively, recursively and incrementally, which is important: “SDLC” does not mean “old-fashioned Waterfall”. (iso.org)
For a European CTO, the SDLC is useful because it connects three layers of control:
- Business control: why are we funding this product, and what value must it create?
- Engineering control: how will we design, build, test and operate it safely?
- Governance control: what evidence proves that quality, security and compliance were handled properly?
A strong SDLC also prevents a common scaling failure. Early-stage teams often move quickly through informal communication. Once the company reaches multiple squads, external suppliers, regulated customers or cross-border operations, informal delivery stops scaling.
The SDLC gives those teams a shared language. Product owners can describe requirements. Architects can record design decisions. Engineers can trace code to backlog items. QA and security teams can test against agreed criteria. Operations can see what changed, when and why.
Security now belongs inside the SDLC. According to NIST SP 800-218, Secure Software Development Framework Version 1.1, finalised on 3 February 2022 and published in February 2022, few SDLC models explicitly address software security in detail, so secure practices usually need to be integrated into each implementation. (csrc.nist.gov)
That is the executive point: SDLC phases should not slow delivery. Done well, they reduce rework, make decisions visible and help teams ship with confidence.
What are the key SDLC phases in a modern software project?
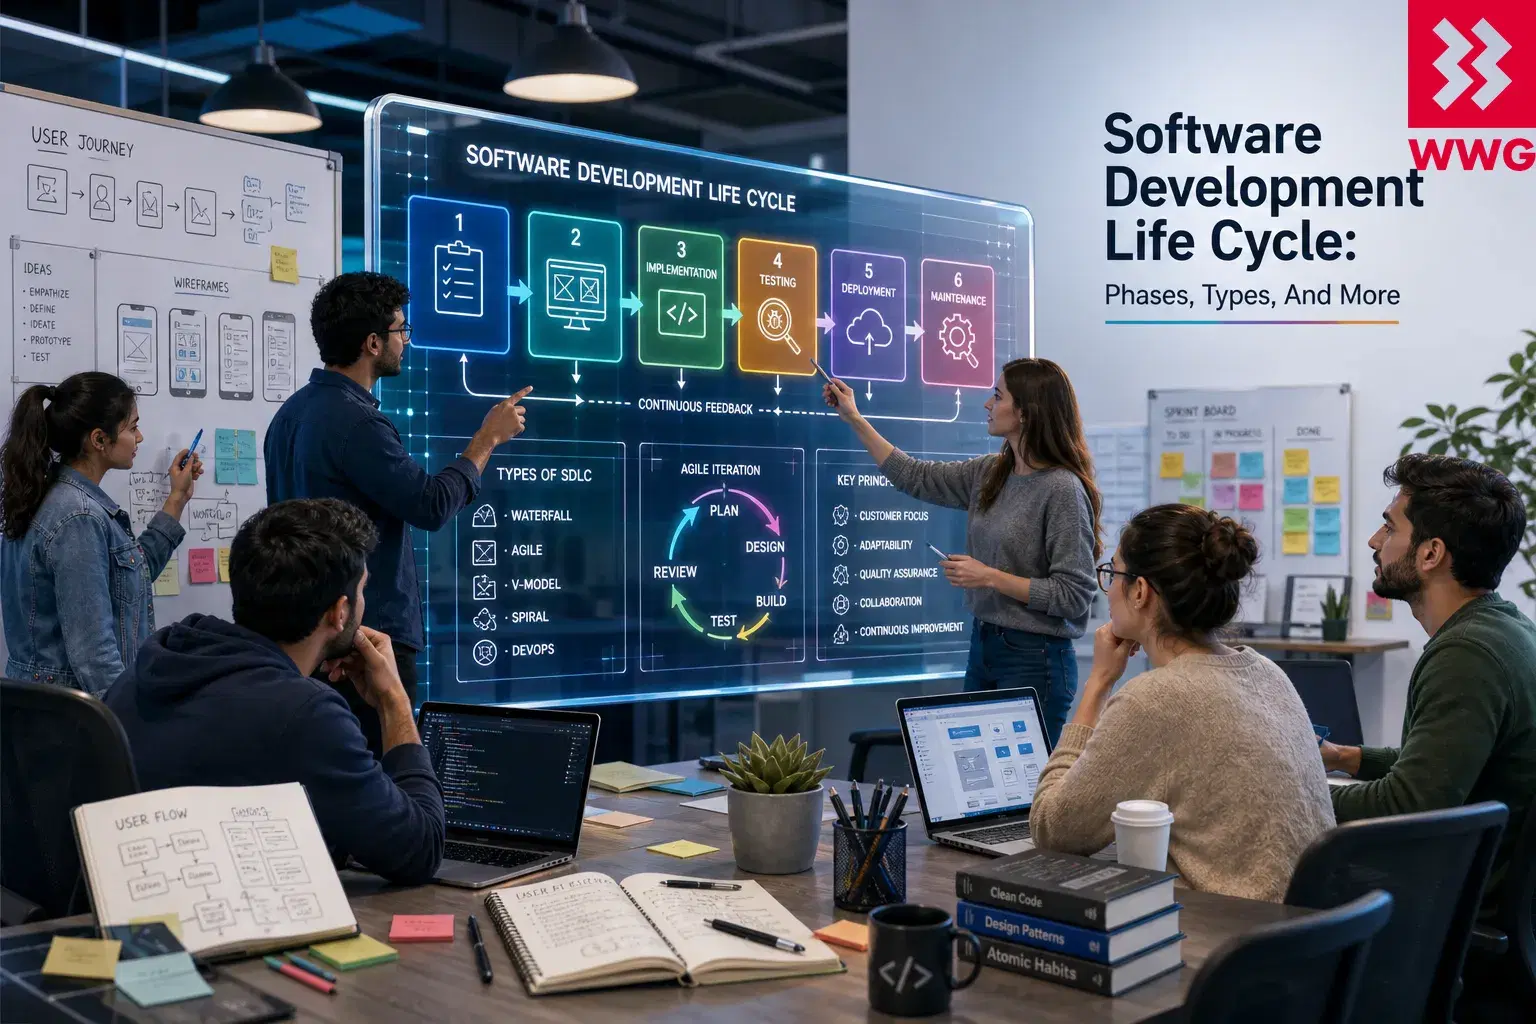
The key SDLC phases are planning, analysis, design, implementation, testing, deployment and maintenance. Each phase answers a different delivery question: why build, what to build, how to build, whether it works, how to release it and how to improve it safely after launch.
These phases are usually shown sequentially, but modern teams often loop through them in short cycles. A Scrum team, for example, may plan, analyse, design, build, test and release a thin product increment inside one sprint.
| SDLC phase | Primary purpose | Typical outputs |
|---|---|---|
| Planning | Define goals, budget, risks and ownership | Business case, roadmap, delivery plan |
| Analysis | Clarify requirements and constraints | User stories, acceptance criteria, domain model |
| Design | Shape architecture and user experience | Solution design, API contracts, UX flows |
| Implementation | Build the software | Code, infrastructure scripts, documentation |
| Testing | Verify quality and risk controls | Test results, defect logs, security findings |
| Deployment | Release into target environments | Release notes, rollback plan, monitoring checks |
| Maintenance | Operate, support and improve | Patches, enhancements, incident learnings |
Planning should define the commercial reason for the work. This includes business outcomes, stakeholders, funding model, delivery constraints and initial risk assumptions. A weak planning phase produces “busy teams” rather than valuable software.
Analysis turns intent into workable requirements. Good analysis distinguishes business rules, user needs, non-functional requirements and compliance obligations. In regulated sectors, this is also where traceability begins.
Design translates requirements into a technical solution. This includes architecture, data flows, integration patterns, security controls, deployment topology and user experience. According to ISO/IEC 25010:2023, the product quality model contains nine characteristics for ICT and software products, giving teams a structured way to discuss quality beyond “it works”. (iso.org)
Implementation is where engineers create the product, but it should not be treated as the only “real” SDLC phase. Coding decisions affect maintainability, observability, resilience and future cost.
Testing should combine automated tests, exploratory testing, performance testing, accessibility checks and security validation. Deployment then moves the change into production through controlled release practices. Maintenance closes the loop by using incidents, telemetry and user feedback to improve the next cycle.
Which types of SDLC models should technology leaders understand?
Technology leaders should understand Waterfall, Agile, Spiral and V-Model first because they represent the main delivery trade-offs: predictability, adaptability, risk management and verification discipline. Most real organisations use hybrids, combining Agile execution with architecture governance, compliance gates and structured release management.
| SDLC model | Best fit | Main limitation |
|---|---|---|
| Waterfall | Stable scope, fixed contracts, heavy documentation | Poor fit for changing requirements |
| Agile | Evolving products and frequent feedback | Needs strong product ownership |
| Spiral | High-risk, complex or uncertain systems | Can be management-heavy |
| V-Model | Safety-critical or verification-heavy work | Less flexible after requirements freeze |
Waterfall runs phases in sequence. It suits projects where requirements are stable, procurement demands formal milestones or contractual acceptance depends on documentation. Its weakness is late feedback: users may not see working software until major assumptions are already expensive to change.
Agile works in short iterations and values working software, collaboration and responsiveness. The Agile Manifesto, published in 2001, established the values behind this movement, including customer collaboration and responding to change. (agilemanifesto.org) The 2020 Scrum Guide by Ken Schwaber and Jeff Sutherland defines Scrum as a lightweight framework for generating value through adaptive solutions to complex problems. (scrumguides.org)
Spiral is risk-driven. Barry Boehm’s 1988 IEEE Computer paper described the Spiral model as an evolving, risk-driven approach for guiding the software process. It is useful when technical uncertainty, safety, architecture or supplier risk must be evaluated repeatedly before committing further investment. (scispace.com)
V-Model pairs development activities with corresponding verification and validation activities. It is common in environments where evidence matters: medical software, automotive systems, defence, embedded systems and other high-assurance domains. IEEE 1012-2024, published in 2024, addresses verification and validation processes across system, software and hardware life cycle processes. (ieeexplore.ieee.org)
For many companies with 50–500 employees, the practical answer is not a textbook model. It is a hybrid: Agile product discovery and delivery, architecture decision records, automated quality gates, documented security controls and release governance proportionate to risk.
How should you choose the right SDLC model for your project?
Choose the SDLC model by assessing requirement stability, regulatory exposure, technical uncertainty, team maturity, release frequency and stakeholder availability. If requirements are fixed, use more predictive controls. If learning is essential, use Agile. If failure would be costly, add stronger verification, risk reviews and security evidence.
Start with six diagnostic questions:
- How stable are the requirements? Stable scope supports Waterfall or V-Model. Volatile scope favours Agile or iterative delivery.
- How severe is failure? The higher the safety, financial, legal or reputational impact, the more verification you need.
- How often must the product change? Frequent market feedback favours Agile, DevOps and continuous delivery.
- Who must approve decisions? External auditors, enterprise customers and public-sector buyers often require evidence.
- How mature is the team? Agile without disciplined engineering becomes uncontrolled change.
- How integrated is the system? Complex dependencies may need architecture governance before sprint-level execution.
According to PMI’s Pulse of the Profession 2024 report, published in February 2024 and based on the PMI Annual Global Survey on Project Management 2023, project teams performed comparably across predictive, hybrid and agile approaches. The same report’s Figure 14 records average reported project performance in 2023 at 73.8%, with average scope creep at 30% and average budget loss for failed projects at 25.7%; this is project-management survey evidence, not a software-only benchmark. (pmi.org)
That distinction matters. Senior leaders should avoid methodology tribalism. Agile is not automatically modern. Waterfall is not automatically wrong. The failure pattern is choosing a model for ideology rather than constraints.
For a SaaS product, use Agile discovery, trunk-based development, automated testing and progressive delivery. For an ERP modernisation, use hybrid governance: upfront architecture, iterative migration waves and formal acceptance criteria. For regulated embedded software, use V-Model discipline with traceability from requirements to tests.
In all cases, build security into selection. According to the European Commission’s Cyber Resilience Act summary, Regulation (EU) 2024/2847 entered into force on 10 December 2024; Article 14 reporting obligations apply from 11 September 2026, and the Act becomes fully applicable from 11 December 2027. That places secure development, vulnerability handling and product evidence directly on the roadmap for manufacturers of products with digital elements. (digital-strategy.ec.europa.eu)
What benefits does a structured SDLC deliver, and what should leaders do next?
A structured SDLC improves predictability, quality, security, auditability and long-term maintainability. The next step is to make the SDLC operational: define decision rights, automate evidence collection, measure flow and quality, and review the model quarterly so it evolves with the product and organisation.
The first benefit is better investment control. Planning and analysis force leaders to define outcomes before capacity is consumed. This reduces the risk of teams building technically competent features that do not change customer behaviour, revenue, efficiency or compliance posture.
The second benefit is quality assurance by design. Testing becomes cheaper when requirements are testable, architecture is reviewable and code is observable. According to CISQ’s press release of 6 December 2022 for The Cost of Poor Software Quality in the US: A 2022 Report, the report estimated the 2022 US cost of poor software quality at $2.41 trillion and accumulated technical debt at approximately $1.52 trillion; this is a US economic estimate, not a European enterprise benchmark, but it illustrates the scale of avoidable quality cost. (it-cisq.org)
The third benefit is risk mitigation. Security, privacy, resilience and supplier risk can be addressed phase by phase. ENISA’s June 2025 technical guidance on the NIS2 Implementing Regulation lists areas such as supply chain security and security in acquisition, development and maintenance for relevant digital infrastructure and ICT service management entities. (enisa.europa.eu)
The fourth benefit is faster onboarding and supplier alignment. A clear SDLC tells internal teams, nearshore partners and vendors how work flows from idea to production. It reduces ambiguity around backlog ownership, coding standards, Definition of Done, release approvals and incident feedback.
To operationalise SDLC phases, leaders should:
- define one lifecycle policy for all software work, with lighter variants for low-risk changes;
- map controls to phases, including OWASP SAMM, NIST SSDF and ISO/IEC 25010 where relevant;
- automate CI/CD, testing, dependency scanning and release evidence;
- track lead time, change failure rate, escaped defects and technical debt trends;
- review the SDLC after major incidents, audits and product pivots.
The most effective SDLC is not the most detailed document. It is the simplest delivery system that gives your organisation speed, evidence and control.
Explore our detailed guides on specific SDLC models to enhance your software development process.
Sources
- ISO/IEC/IEEE 12207:2026, Systems and software engineering — Software life cycle processes: https://www.iso.org/standard/90219.html
- NIST SP 800-218, Secure Software Development Framework Version 1.1: https://csrc.nist.gov/pubs/sp/800/218/final
- European Commission, Cyber Resilience Act — Summary of the legislative text: https://digital-strategy.ec.europa.eu/en/policies/cra-summary
- CISQ, Cost of Poor Software Quality in the US: A 2022 Report press release: https://www.it-cisq.org/press-releases/12-06-22/
- PMI, Pulse of the Profession 2024 — The Future of Project Work: https://www.pmi.org/learning/thought-leadership/future-of-project-work
- ISO/IEC 25010:2023, SQuaRE — Product quality model: https://www.iso.org/standard/78176.html
- Agile Manifesto, 2001: https://agilemanifesto.org/
- Scrum Guide, 2020: https://scrumguides.org/scrum-guide.html
- Barry W. Boehm, A Spiral Model of Software Development and Enhancement, IEEE Computer, 1988: https://doi.org/10.1109/2.59
- ENISA, Technical implementation guidance supporting NIS2 implementation, June 2025: https://www.enisa.europa.eu/news/supporting-nis2-implementation-through-actionable-guidance
FAQ
Frequently Asked Questions
Quick answers for technical leaders evaluating SDLC phases, models and delivery governance.